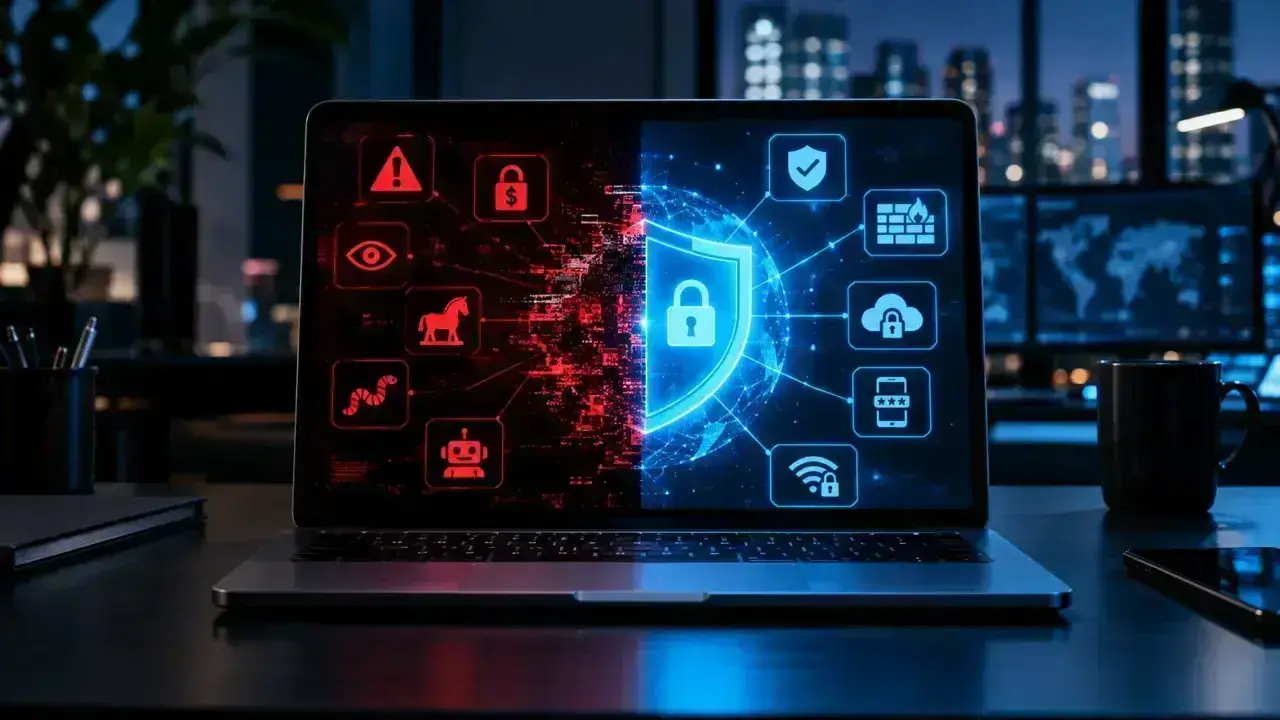
Malware is malicious software or code created to harm devices, disrupt systems, steal information, spy on users, or give attackers unauthorized control. The term covers many threats, including viruses, worms, Trojans, spyware, ransomware, adware, rootkits, bots, and fileless attacks. Malware can affect computers, smartphones, tablets, and business networks, and attackers use it for everything from financial theft to espionage and extortion.
These programs infiltrate memory and storage to exfiltrate private data, hijack resources, disrupt workflows, or extort victims. Malware operates in the background or restricts system functions, a consistent risk to individual users and enterprise environments.
What is the Purpose of Malware?
Malware is rarely built without a goal. Attackers build it to steal assets, disrupt operations, maintain hidden access, or convert compromised devices into staging points for further strikes.
To Steal Information
Some malware harvests passwords, financial data, private messages, browsing history, and sensitive documents. Data theft is not a smash-and-grab; it is quiet observation, and Spyware and keyloggers excel in this surveillance. Once executed on a device, they operate in the background without obvious red flags or disruption to daily tasks.
Keyloggers record what you type to steal your passwords, card numbers, and confidential messages. Spyware goes further by scraping your browser history, saved logins, and personal files. These tools send your data to a remote server, giving attackers a window into your digital life while you stay completely unaware of the breach.
Disrupt Systems and Demand Payment
Ransomware is developed to disrupt and extort. It can encrypt files or block access to critical systems, then demand money to restore functionality.
But lately, attackers have stepped up their game with a “double extortion” tactic. Instead of just locking data, they also steal a copy of your sensitive information and threaten to leak it publicly unless you pay the ransom. This puts a lot more pressure on victims, since even if you have backups and can restore your files, the threat of a public data breach remains.
Destroy or Damage Infrastructure
Some malware is designed to interfere with systems rather than generate direct financial returns. Attackers may use it to damage data, disrupt operations, or compromise critical network infrastructure.
Beyond direct financial hits, some malicious software is built strictly to break things and keep them broken. For example, wiper malware—like the NotPetya attack—can permanently delete master boot records or scramble file systems, making hardware completely unresponsive. When malware targets critical infrastructure like power grids, manufacturing control systems (ICS), or hospital record databases, operations grind to a halt because the underlying systems can no longer communicate or function.
This impacts continuity because it forces businesses to switch to emergency manual processes or total downtime. Long-term recovery is painful. IT teams often have to wipe and rebuild servers from the ground up, audit the integrity of every piece of data, and physically replace corrupted hardware. This process drags on for weeks or months, and during that time, the company’s reputation suffers, and it may even face legal or regulatory fallout for failing to provide required services.
Abuse Computing Resources
A compromised device can become a valuable asset for an attacker, and the innocent owner remains unaware. Your computer or smartphone might become a bot used in massive distributed denial-of-service attacks. Hackers can also take over your processor to mine cryptocurrency, draining your power and reducing system performance while sending the profits elsewhere. In other cases, infected devices are used to send spam, distribute malicious content, or support additional attacks. By controlling many vulnerable systems at once, cybercriminals can build a powerful hardware network without spending a dime.
How Does Malware Spread?
Hackers use many ways to infect your devices. They often target you through email, websites, apps, messaging tools, bad ads, hardware like USB drives, and security holes in your software.

Phishing and malicious email attachments are common entry points. A victim might open a seemingly legitimate document or click a deceptive link and unknowingly execute malicious code. Malware can also spread through spam websites, fraudulent applications, unsafe downloads, infected USB devices, or legitimate sites with malicious ads.
Software flaws are another common entry point. An exploit abuses a vulnerability in an operating system, browser, application, or other component to bypass security controls and deliver malicious code. Exploit kits make this easier for them by finding your weak spots and launching automated attacks.
Mobile users face many of the same risks. Attackers target your device through bad links, shady texts, emails, and compromised apps. Avoid software downloads outside official stores because hackers often hide malware inside tools that look helpful, only to trick you.
Types of Malware

Think of malware as a big umbrella term. Because these threats are so different from one another, they often work in layers to get the job done. Attackers love using “blended threats” to sneak past defenses. For example, they might use a Trojan to trick you into downloading a keylogger, which then quietly introduces a ransomware payload in the background. Although there’s no shortage of malware types nowadays, here are a few of the most common.
Viruses
A virus is executable code that attaches to a legitimate host file, program, or document and generally requires the infected content to be opened or executed to spread. It remains dormant until a user triggers it, after which it can modify other files, replicate its code, corrupt data, or interfere with normal system operation.
Worms
Worms differ from viruses because they can spread from one system to another without attaching themselves to another program. They mostly exploit security weaknesses or network connections and replicate automatically. It enters a device via a downloaded file or a network connection, then multiplies at an exponential rate. Just like a virus, these programs affect device performance and cause data loss. A fast-spreading worm can consume network resources, disrupt services, and deliver extra malicious payloads.
Trojans
A Trojan disguises itself as legitimate or useful software or a benign utility application. The victim installs it voluntarily, believing the program is safe, while the malware creates backdoors to steal data, download secondary payloads, or give an attacker remote access. Unlike worms, Trojans do not normally spread by self-replication.
Spyware
Spyware is unobtrusive malicious software that secretly observes users and sends collected details to another party. Depending on the implementation, it can track browsing behavior, capture credentials, monitor communications, or record other activity. Keyloggers are a notable example because they capture what a user types, potentially exposing usernames, passwords, and financial details.
Adware
Adware is aggressive advertising code that displays unwanted ads, commonly through pop-ups or browser activity. Not every ad-supported program is malicious, but strong or deceptive adware can change browser settings, slow a device, redirect users to dangerous websites, or arrive alongside spyware and other unwanted software.
Ransomware
Ransomware is extortion malware that encrypts critical storage files or locks device access, holding system data hostage until you pay the asked amount. Modern attacks can involve far more than an infected file. Attackers can first steal credentials, enter a business network, move through connected systems, and identify valuable data before deploying the ransomware. Some groups now operate this as a service, letting developers build the tools while separate teams carry out intrusions.
Rootkits
Rootkits are deeply embedded software that remain hidden while giving attackers deep or elevated access to a system. By interfering with normal operating system processes, a rootkit can conceal programs, processes, or other evidence of compromise. Persistent rootkit access can allow attackers to spy, steal data, and install additional malware.
Bots and Botnets
A bot is malware that enables automated malicious activity, while a botnet is a network of infected devices controlled by an attacker. Botnets can send spam, steal information, mine cryptocurrency, or launch distributed denial-of-service attacks against other systems.
Cryptojacking
Cryptojacking is unapproved code that secretly uses a victim’s processor or other computing resources to mine cryptocurrency for cybercriminals, severely degrading device performance and draining power reserves. Because mining consumes massive processing power, infected systems might become noticeably slow, hot, or less responsive. Attackers often seek large numbers of compromised devices to make the operation profitable.
Fileless Malware
Fileless malware is a memory-resident threat that executes in a PC’s RAM using trusted operating system tools, leaving no traditional files on the hard drive for normal scanners to detect. It usually finds a flaw in your system to sneak through the door. Instead of dropping a suspicious program file, it highjacks safe, regular programs already running on your machine. Without a physical file to flag on the disk, standard security scans get bypassed that makes this cyberthreat hard to detect and even harder for security experts to investigate afterward.
What are the Signs of a Malware Infection? How to Detect Threats

Malware is not always obvious. Some threats deliberately stay under the radar, so the absence of dramatic symptoms doesn’t necessarily mean a device is clean. Even when things look normal, infected systems show specific warning signs.
- A system becomes slow or unresponsive.
- Applications crash or the operating system freezes unexpectedly.
- Pop-ups appear frequently, including when the browser is closed.
- New applications, extensions, or programs appear without authorization.
- Browser settings, such as the homepage or search engine, change unexpectedly.
- Unexplained spikes in outbound internet traffic or data plan consumption.
- A device becomes unusually hot, or its battery drains much faster than normal.
- Security software is disabled or won’t operate.
- Files become inaccessible or are replaced by a ransom message.
- Unusual outbound network traffic suggests a hidden program is communicating with an attacker’s server.
How Does Malware Affect Businesses?
For organizations, malware can create damage well beyond the infected endpoint. When a device or network is compromised, the ripple effects usually fall into three categories:
- Financial Drain: The immediate costs can pile up fast. Beyond the obvious risk of paying a ransom, you will face expensive investigation fees, security expert costs, and the time and money to rebuild your systems from scratch. For businesses, these expenses can spiral out of control in a matter of days.
- Theft of Sensitive Data: Malware is designed to steal what’s valuable. Attackers mostly target the most sensitive assets, including private customer information, confidential intellectual property, and login details. Once this data is out in the wild, it’s not only your privacy that’s gone; you also face a high risk of identity theft and corporate espionage.
- Long-Term Damage to Trust: Perhaps the worst part is what happens after the initial attack. Extended downtime forces operations to a standstill, leaving you unable to serve users or clients. If your systems stay offline for too long, or worse, if word gets out that your customers’ data was exposed, your reputation can take a massive hit. Rebuilding the lost trust is much harder and takes longer than fixing the technical side of the breach.
The risk becomes greater when malware moves from one device into your entire network. A single infected laptop gives hackers a path to move sideways into your cloud services, company apps, and shared infrastructure. On top of that, people often use their personal phones for work without realizing they’re creating a big security hole, one that could easily expose business logins and private company data to hackers.
How to Prevent Malware Attacks
Strong malware protection depends on several layers of security. One control can fail or be bypassed, so organizations should combine prevention, detection, access controls, user awareness, and recovery measures.

Use Reputable Security Software
Antivirus and endpoint security software can scan files and links, block known threats, spot suspicious activity, and isolate or remove malicious programs. Protection should cover computers as well as phones and tablets.
Keep Systems and Applications Patched
Security updates close vulnerabilities that attackers may otherwise exploit. Operating systems, browsers, applications, plugins, and security products must always remain up to date, ideally through automatic updates where possible.
Be Careful with Links, Attachments, and Downloads
Ignore urgent messages that demand you open attachments or click links. Avoid software from untrusted sites and be cautious with applications distributed via unofficial stores or direct download links.
Check Application Permissions
Be cautious when an application asks for access to information or device functions that are unrelated to what the app is supposed to do. Before installing it, check the developer, requested permissions, download history, and user reviews.
Use Strong Authentication
Strong, unique passwords combined with multifactor authentication (MFA) reduce the damage caused by stolen credentials. A good password manager makes it very easy to keep all your logins safe without the headache of trying to remember them all.
Train Users Regularly
Your team is your first line of defense, so keep everyone in the loop with regular security training. Teaching your staff how to spot phishing emails, sketchy links, and social engineering scams can make a lot of difference in protection against malware. If you can arrange a few practice simulations, it can help users identify these threats in practice.
Maintain Reliable Backups
Backups are crucial against destructive malware and ransomware. Keep some copies offline or disconnected from your main network so an attacker cannot wipe or encrypt everything at once. Make sure to test these backups too, because a file you cannot restore is useless.
Adopt Zero Trust Principles
Zero Trust assumes no user or device is safe by default until they meet the required security conditions. Access decisions can be based on identity, device health, and risk that limits the chance for compromised accounts or endpoints to move freely through an environment. Multifactor authentication is just one part of this approach.
How to Detect and Respond to Malware
Most security setups eventually fail at the boundary. Catching an intrusion requires looking for odd behavior that slips past the initial barriers.
Organizations usually rely on a layered security approach to stay safe. Instead of depending on one tool, they combine many, including antivirus software, EDR (endpoint detection and response), XDR (extended detection and response), MDR (managed detection and response), firewalls, and SIEM (security information and event management) systems.
While EDR keeps a close eye on what’s happening at the individual device level, XDR goes a step further by connecting the dots across your entire network, including emails, user accounts, and cloud apps, to give security teams a better picture of potential threats. To stay one step ahead of hackers, many companies also lean on MDR services. This brings in experts who consistently monitor for suspicious activity and neutralize complex threats before they can do any real damage.
When a compromise is suspected, the priority is to contain it before the attacker can spread further. Disconnecting an affected device from the network can limit communication and lateral movement. Security teams should then investigate the source, identify affected systems, remove the dangerous parts, reset potentially exposed credentials, patch exploited weaknesses, and verify that systems are clean before restoring normal access.
A clear incident response plan changes how a team handles a breach. It should define who is responsible for detection, containment, investigation, communication, recovery, and post-incident review. When an attack happens, time is the enemy. Decisions made on the fly are often flawed, but if your team knows who is in charge of communications and who manages system logs, the response will be fast. You also need a plan for the aftermath. A post-incident review helps you understand what failed and why; this is how you fix your security gaps.
What Should You Do After a Malware Infection?
If you think you have fallen victim to malware, act fast to contain the damage. Unplug the device from your network, and run a scan with trusted security software to remove or quarantine anything malicious. Update your OS and security tools, then run another scan to be sure. You should also change your passwords, especially for your email, bank, and any cloud accounts that might have been attacked.
In an office setting, follow your company’s incident response plan. IT teams need to figure out how the malware was injected, what accounts or systems were accessed, if any data was stolen, and if other machines are infected. Tools like SIEM, EDR, and XDR are your best way to spot patterns across the network.
How Malware is Evolving
Cybercriminals have mostly abandoned the old playbook and no longer rely on static files that antivirus programs can easily flag. Instead, they write code that morphs, hides inside standard system processes, or lives completely in volatile memory. By the time a security scanner completes its check, the threat has often changed its shape or vanished from the disk. This shift renders traditional signature-based detection outdated. Relying on a database of known threats is a losing battle when attackers generate unique versions of their code for every target.
Defenders now look for behaviors instead of specific file traits. They monitor system activity to catch suspicious patterns. If a normal app out of nowhere tries to connect to a random server or inject code into your browser, the system flags it right away. Analysts rely on these anomalies to catch intruders. Machine learning models help cut through the noise by flagging deviations from established baselines to keep the defenders focused on real threats.